On 17 September 2024, thousands of small pagers carried by members of Hezbollah went off almost at the same moment across Lebanon. The next day, a second wave hit hand-held radios. Hospitals filled with people wounded in the hands, faces and eyes. Bystanders in shops, streets and cars were caught up too.
Two years on, the Lebanon pager explosions still raise a question that reaches far beyond the region: if an ordinary electronic device can be turned into a weapon before it ever reaches its owner, what does that say about the gadgets the rest of us buy, carry and rely on?
This guide sets out what is publicly known, where the facts are still contested, and why the story matters for anyone who depends on technology to work, whether you are a freelancer, remote worker, job seeker or small business owner. It then offers a practical, step-by-step approach to supply chain and device security in your own life. To be clear from the start: this was a targeted state operation against a specific group, not a threat to the average consumer.
What Are the Lebanon Pager Explosions?
The Lebanon pager explosions were a coordinated series of detonations of pagers on 17 September 2024, followed by walkie-talkies on 18 September. They struck people in Lebanon and, in some reports, Syria.
Here is what reliable reporting supports:
- The devices had been newly acquired. Hezbollah’s leader had reportedly told members to stop using mobile phones because of tracking fears, and pagers were brought in as a lower-tech alternative.
- The devices appear to have been rigged before delivery. Lebanon’s mission to the United Nations told the Security Council that its preliminary investigation found the devices had been tampered with by foreign entities before arriving in the country.
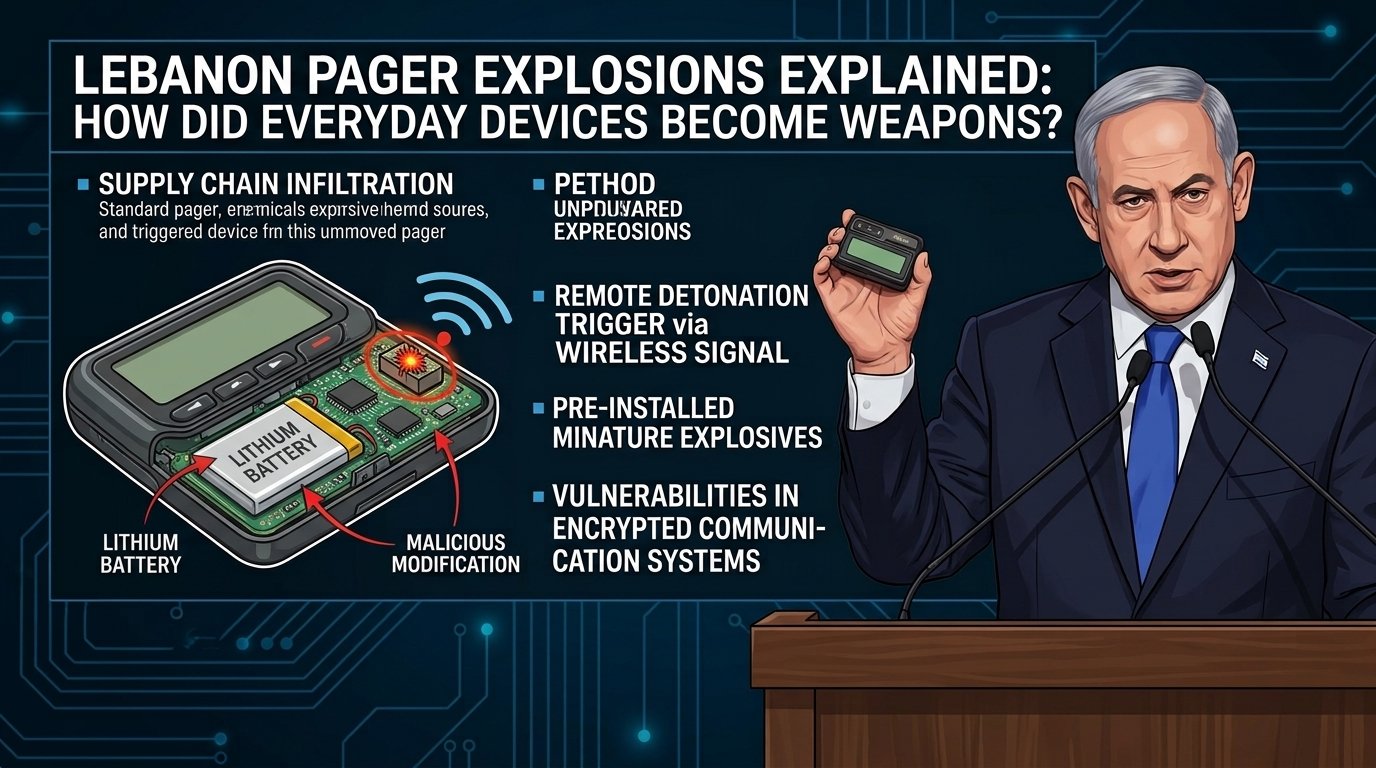
- Experts pointed to the supply chain, not a simple hack. Most specialists said the blasts were unlikely to be the result of a software bug overheating batteries. The pattern was more consistent with explosive material hidden in the devices and triggered remotely.
- Israel was widely blamed. The Israeli government did not confirm involvement at first. In November 2024, the prime minister’s spokesperson said he had approved the operation.
Casualty figures differ by source and date. UN human rights experts, speaking on 19 September 2024, cited at least 32 deaths and about 3,250 injured across both days. Lebanese health authorities later cited roughly 37 to 39 deaths. The Associated Press has reported that the first wave killed 12 people, including two children, and wounded more than 3,000. Hezbollah has said most of the casualties were its personnel, but civilians were also hurt.
The legality of the operation is disputed. UN experts called it a violation of international law and described the attacks as indiscriminate, while Israeli officials presented it as a strike against a militant group. This article does not take a side; it focuses on the technology and security lessons.
How Did Everyday Devices Become Weapons?

The key idea is the supply chain attack. Any electronic device is the product of many hands: one factory may make the battery, another the chips, another the casing, and a final assembler puts it together. Brands are sometimes licensed to other manufacturers, and resellers and shipping companies add more links.
In reporting on the Lebanon pager explosions, the brand on the pagers was linked to a Taiwanese company, which said it had licensed its name and had no role in making them. Investigators and journalists pointed to a Hungarian firm and a web of intermediaries. Details were murky then and remain partly unverified, which is itself a lesson: long supply chains are hard to audit, even for people who are trying.
Security experts said the tampering could, in theory, have happened at several points along that chain. A trusted supplier does not have to be malicious for a device to be compromised; someone only needs a way in.
The episode also fed a wider debate. Analysts noted that it gave fresh urgency to government efforts to reduce dependence on technology from rivals, and it pushed companies to ask harder questions about where components come from and who handles them on the way. For a small business, the equivalent question is far simpler: do you know who you are buying from, and would you notice if something looked wrong?
Step-by-Step Guide: How to Apply the Lessons of the Lebanon Pager Explosions to Your Own Devices

You are extremely unlikely to face anything like this. But the same principle, trust in what you buy, applies to everyday risks such as counterfeit chargers, tampered accessories and outdated firmware. Here is a sensible, proportionate approach.
Step 1: Put the Risk in Proportion
What to do: Remind yourself what the Lebanon pager explosions actually were: a carefully planned, resource-heavy operation aimed at one organisation’s procurement channel.
Why it matters: Fear leads to bad decisions. The realistic risks for most people are counterfeit batteries, insecure gadgets and phishing, not booby-trapped consumer goods.
Example: A freelancer worried about exploding phones would do better to spend that energy on strong passwords, backups and updates, which protect against the problems that actually affect people.
Step 2: List the Devices You Depend On

What to do: Write down every device you use for work: laptop, phone, router, external drives, headsets, chargers, smart speakers.
Why it matters: You cannot protect what you have not counted. A simple inventory also shows which items are old, unsupported or bought from questionable sellers.
Example: A remote worker might find a five-year-old router that no longer receives security updates.
Step 3: Know Where Your Gear Comes From
What to do: For each important item, note the seller and channel. Prefer the manufacturer, authorised retailers or established stores.
Why it matters: The pager story shows how hard it can be to trace who made what. Buying through reputable channels reduces the number of unknown hands.
Example: A very cheap power bank from an unknown marketplace seller is a bigger practical risk than a laptop from an authorised shop.
Step 4: Inspect Packaging and Products

What to do: Check sealed packaging, tamper stickers, serial numbers and general build quality when new gear arrives. Return anything that looks opened, damaged or oddly assembled.
Why it matters: Simple checks catch counterfeits and obvious tampering, even though they cannot catch a sophisticated attack.
Step 5: Keep Software and Firmware Updated
What to do: Turn on automatic updates for operating systems, apps, routers and other connected devices.
Why it matters: Most real-world compromises exploit known, patchable flaws. Updating is the most effective everyday defence.
Step 6: Limit What Each Device Can Access
What to do: Use separate accounts, strong unique passwords, two-factor authentication and, where possible, a separate device or profile for sensitive client work.
Why it matters: If one item is compromised, limited access keeps the damage small. This is the same “assume something can fail” thinking that security professionals use.
Step 7: Replace Damaged or Swollen Batteries
What to do: Stop using any device with a swollen, hot or leaking battery, and dispose of it through a proper recycling point.
Why it matters: Ordinary lithium battery failures do happen and are unrelated to the events in Lebanon. Treating them seriously protects your home and your work setup.
Step 8: Build Security Skills Carefully
What to do: If this topic interests you professionally, consider learning the basics of supply chain risk, procurement security or general cybersecurity through reputable courses.
Why it matters: Organisations are paying more attention to vendor and hardware risk. That said, learning these skills does not guarantee any job, client or income, and results depend on your background and market.
Common Mistakes to Avoid
- Treating rumours as facts. Early social media claims about the Lebanon pager explosions, including hacked batteries, were later challenged by experts. Check reliable sources.
- Assuming your own gadgets are at risk. This was a targeted operation, not a general consumer threat.
- Ignoring boring security basics. Updates, backups and unique passwords matter far more for most people.
- Buying the cheapest unknown-brand electronics. Low price often means weak quality control.
- Forgetting human impact. Behind the technology story are injured and bereaved people, including bystanders. Discuss it with care.
Useful Tips
- Read more than one credible news source and note where they disagree.
- Distinguish confirmed facts from allegations and from official claims.
- Keep receipts and serial numbers for important equipment.
- Ask employers or clients about their approved-device policies.
- If you run a small business, add “where does this hardware come from?” to your purchasing checklist. For wider habits, see our guide to protecting your devices when working remotely.
Frequently Asked Questions
Were the pagers hacked? Most experts said this was not an ordinary hack. The evidence pointed to hidden explosive material placed in the devices before delivery and set off remotely, though full technical details have not been publicly verified.
Who was responsible? Israel was widely blamed and did not initially comment. In November 2024, the prime minister’s spokesperson said he had approved the operation.
Was the operation legal? That is disputed. UN experts described it as a violation of international law and criticised its indiscriminate effects, while Israeli officials framed it as targeting a militant group. You can read the statement by UN human rights experts for one perspective.
Could something like the Lebanon pager explosions happen to my phone or laptop? It is extremely unlikely. The operation required deep access to one group’s supply channel. Everyday device risks are much more mundane.
Why does supply chain security matter to freelancers and small businesses? Because you depend on hardware and software made by others. Sensible buying and updating habits protect your work without requiring technical expertise.
Final Thoughts
The Lebanon pager explosions showed how a trusted, ordinary object can be turned into a weapon when the path from factory to user is compromised. They also showed how difficult it is to trace long supply chains, and how contested the facts, casualties and legal questions remain.

For most of us, the practical takeaway is modest but useful: buy from reputable sources, keep devices updated, limit access, and treat unverified claims with caution. Take one step this week, such as listing your work devices and checking which ones no longer get updates, and you will be more secure than most people ever bother to be.